AI chats
Copilot, ChatGPT, Claude, Gemini
task2mask automatically detects and masks sensitive information in chats, documents, AI agents and API traffic. It works exactly the way you need, based on your own security rules.
Copilot, ChatGPT, Claude, Gemini
DOC · XLS · PPT · PDF · IMG
Automations and agent workflows
Integrations and tool calls
Where task2mask works
One module or all at once: shared policy and log, data stored locally in agreed infrastructure. 100% protection, 0% surveillance - no scanning of private conversations.
It actively monitors AI agents in the browser, preventing the disclosure of sensitive personal and business data. It enforces the agreed rules and anonymises the data. It monitors the list of approved AI providers, so your company uses only the AI you allow.
Chrome and Safari, all plans
A module that anonymises data in attachments. Sharing attachments? Your AI provider doesn't need to know details unrelated to the tasks you assign.
Pro plan and above
Working with agents through desktop apps or the terminal? The app passively reports events based on your organisation's rules. Stay up to date on security events as they happen.
Pro plan and above


Who it's for
It matters most where data is sensitive by nature: finance, healthcare and law firms. But almost every company has personal data in its prompts.
The full content and masking map of every conversation stay on your side, so when an audit or a GDPR request comes, you have something to show. Private content is revealed only with a stated reason, which goes to the audit trail too.
A live alert when a secret or a leak attempt shows up in a prompt. Policies set per provider, with no new tool to learn.
Full control over what data reaches AI, without banning the tools. task2mask masks personal and confidential data before it reaches the AI providers. Every event stays in the audit trail, which makes it easier to demonstrate GDPR and AI Act compliance.
You work in the AI tools you know, just as before. In the background task2mask swaps sensitive data for placeholders and restores it in the answer. You don't have to remember what you mustn't paste.
AI driving licence
Only what was actually sent counts, not what someone started typing. Points build up on the employee's balance, as on a driving licence, and once they pass the threshold, access to AI is suspended.
Point tracking and ready-made courses on the Standard plan and above; access suspension and custom courses on the Pro plan and above.
The audit report is available on the Standard plan and above.
Evidence
The report is built from what the system actually recorded, not from a policy document.
A Statement of Applicability (SoA) with controls from policy and identity to training, ready to hand to the auditor.
Each control comes with records from the system: what went to the model, what was masked, who revealed private content and why.
If something needs work, the report says "passed with findings" instead of pretending everything is at 100%. Export to PDF or JSON, with names pseudonymised if you want.
Problem
Shadow AI is employees using external AI tools for work without the knowledge, consent or oversight of IT, security or legal. It usually comes from the absence of AI usage rules: people simply want to get the job done faster and better.
Risks
Personal data of customers and employees ends up in public AI tools, and the company loses control over what exactly leaves the building.
Source code, contracts and product plans end up on external servers, and once an asset has been shared there's no way to pull it back.
Company secrets, unique know-how, technical data or commercial arrangements go straight into cloud AI models in plain form.
Feeding data into public AI can break NDAs, AI Act rules and sector regulations, exposing the company to penalties and claims.
The organisation doesn't know what information actually left the company: there's no record of who asked what, which data they shared, or what came back in response.
Shadow AI
This is Shadow AI: people using AI for work without the organisation knowing. Four ordinary requests from a single day, each carrying data that should never leave the company.
Marketing pastes a list of leads into ChatGPT, with names, emails and phone numbers.
A lawyer asks Claude about a clause from contract no. 2024/118, counterparty name included: Nordic Trading Ltd.
A developer pastes a code snippet into Cursor "just for a second". Inside it is the access key to the production environment.
HR asks the model for an opinion on an employee: Rachel Turner, annual review 4.2/5.
task2mask vs Shadow AI
Step by step
Before the model provider sees a single character, every employee prompt goes through each of them.
Book a demoThe prompt doesn't go straight to the model provider. A browser extension, a portal or a CLI sends it to your company's proxy.
National Insurance number, VAT number, account number, phone, secret: each becomes a consistent placeholder across the whole conversation, e.g. [[NI_NUMBER_1]]. The reply comes back with the real data filled in.
task2mask scores every prompt. Plain data goes to the private log, and a secret or exfiltration attempt raises an alert security sees live.
The admin decides what is allowed and what is blocked, separately for each provider. If the config can't be read, task2mask switches to observe mode: protection keeps running, nobody is cut off from AI.
The full content and masking map stay local, ready for investigations and GDPR requests. The model provider only sees placeholders.
How it works
An employee types as usual. On the way, task2mask swaps the data for placeholders, checks the rules the admin set for that provider and keeps a full copy on your side. Whatever the rules allow goes to the model. task2mask blocks the rest.
Draft an employment contract
for John Carter[[PERSON_1]],
NI number QQ 12 34 56 C[[NI_NUMBER_1]].
task2mask hid the data before the provider saw it.
Every hit gets a confidence score.
The admin sets the rules for each provider.
The model gets the masked version. The full copy stays with you.
In practice
An employee sent an article poster to an AI and asked what it was about. The model described the topic and the author's role correctly, but never got the name, the company or the face.
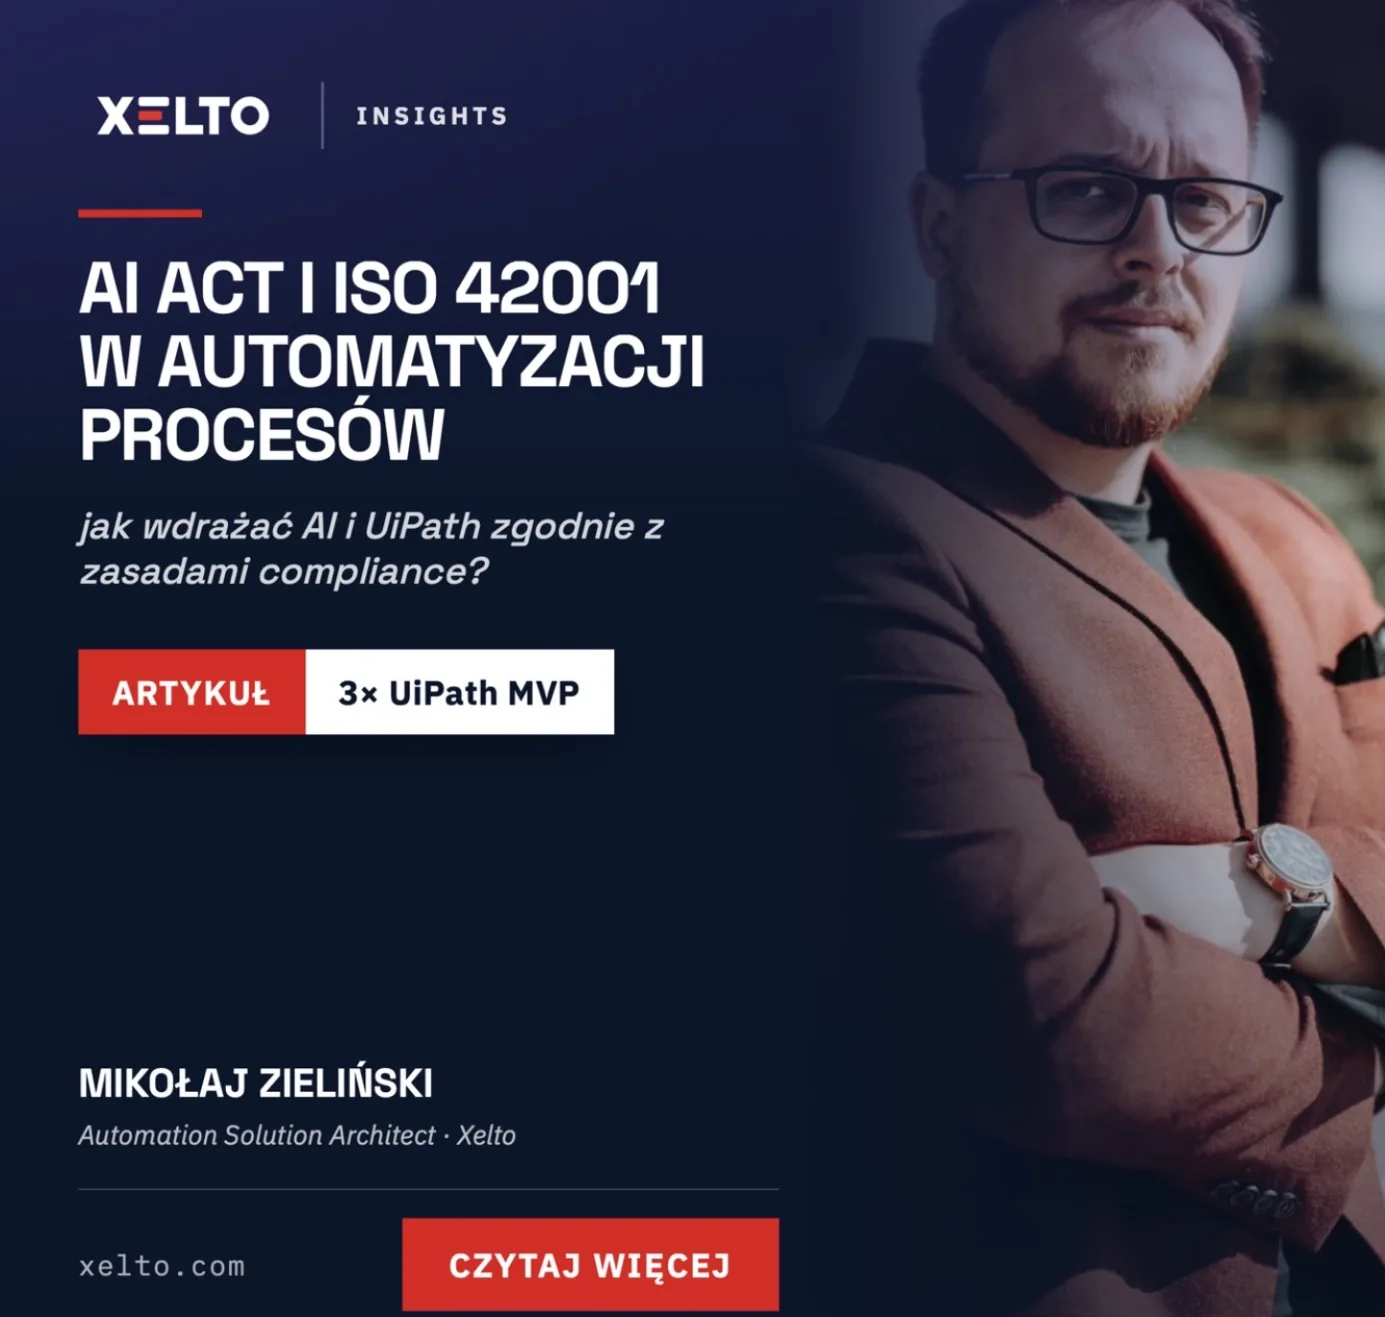
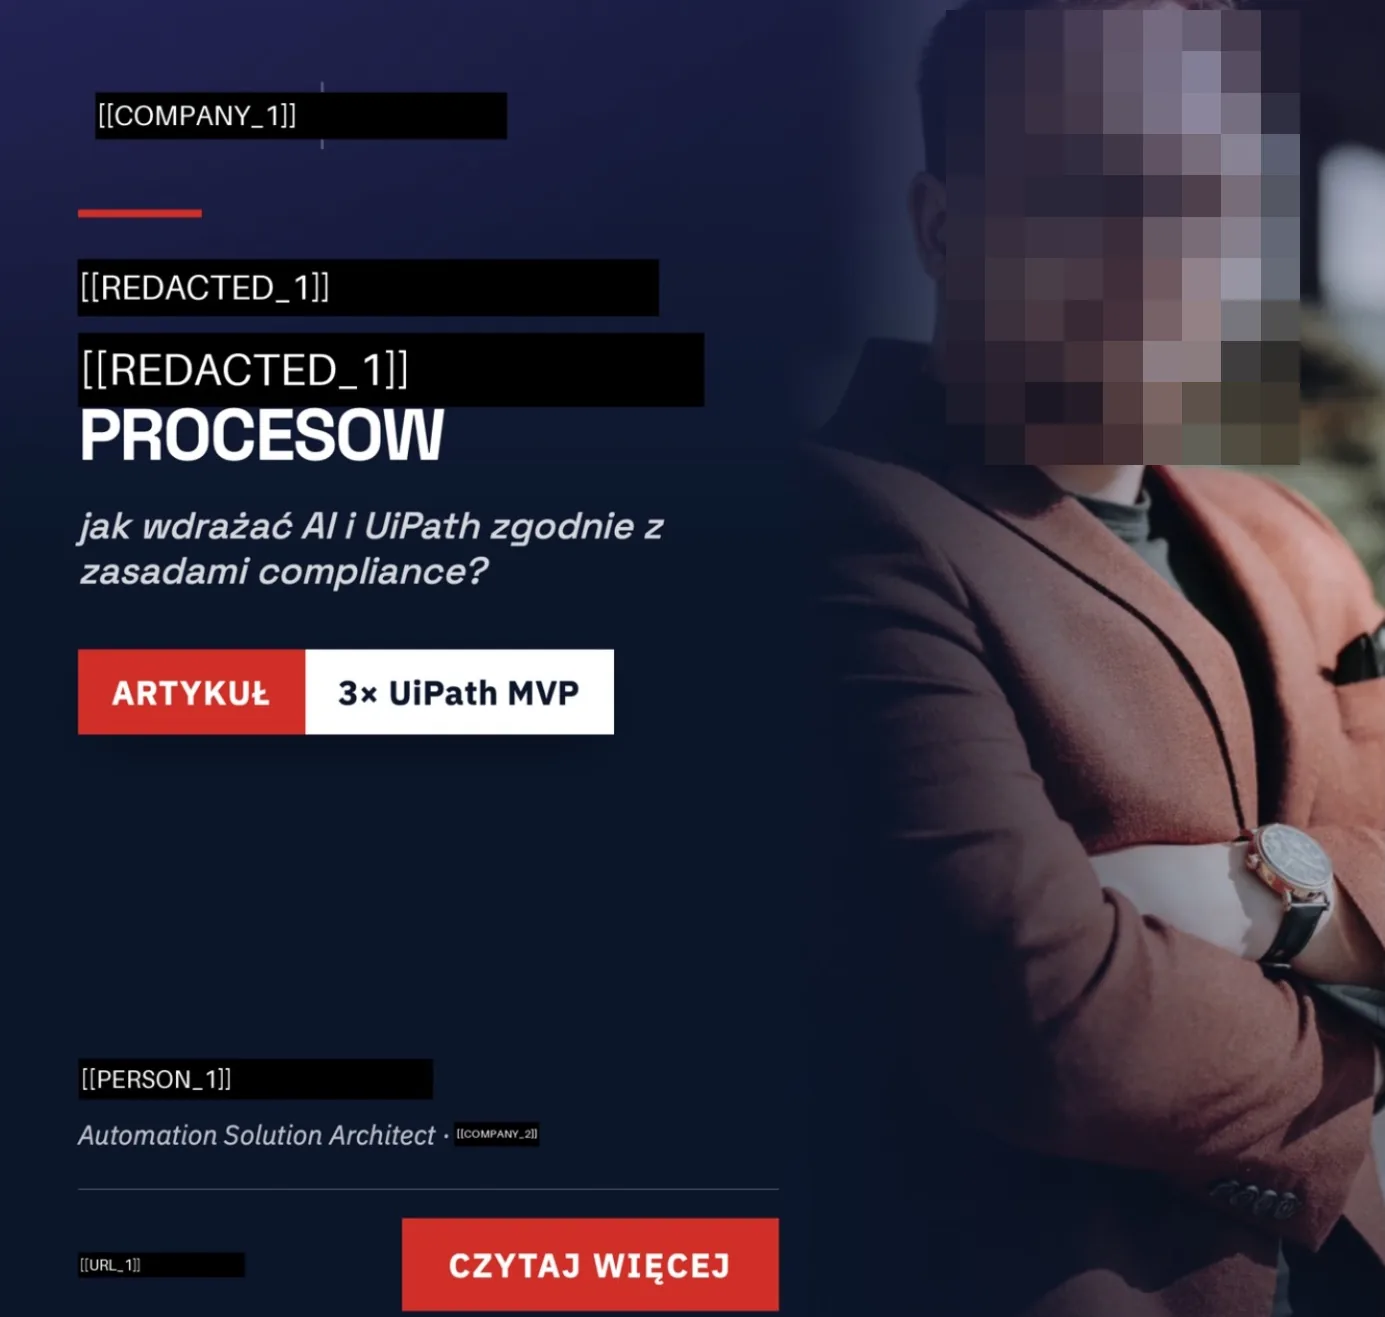
Learning from your own data is available on the Standard plan and above.
Under the hood
task2mask doesn't rely on a fixed list of regular expressions. It learns from incidents and gives every hit a confidence score, so borderline cases go to review.
Someone has to write and maintain a rule for every new data format. A rule nobody added means data that goes through unmasked.
There are patterns underneath too, but nobody writes them by hand. The system uses incidents to build better variants, checks them against test data and deploys only those that improve detection.
Why us
Other tools redact: the data is lost to both the model and the user, so people start working around the tool. With task2mask, the AI provider never sees real data, and the user gets the full text back.
A forensic tool confirms that the original can't be recovered from an anonymised document. A cryptographic chain protects the audit log, so any change to an entry shows up at once.
We process data in infrastructure agreed with you and recognise names and scans locally. Detection is multilingual, down to inflected name forms.
Security & trust
task2mask supports compliance with GDPR, the AI Act and NIS2. Personal data is masked before it reaches the AI, permissions are tied to role and department, and every action goes to the log.
Personal data is masked before it reaches the AI model.
A person makes the decision, and every action stays in the log.
Under NIS2, leadership is accountable for cybersecurity. Permissions are per role and department, and access to data is auditable.
Counterparty names and contract data are masked before they reach the AI.
Xelto's certificate for information security management.
Security features
Your people already use ChatGPT, Claude and Copilot. The question isn't whether to use AI, but how to do it safely. task2mask sits between your people and AI models. Your organisation sets the rules, not the tool vendor.
Book a demoYou decide which AI tools your people use and on what terms. Changes take effect at once.
You choose which data is masked before it reaches the AI. The model never sees the real data.
We only protect traffic to AI services. Employees' private activity is none of our business.
Only an authorised person can see conversation content. The employee always knows who viewed it.
Every action leaves a trace in the event log. You're always ready for an audit.
Alternatives
Every obvious fix ends the same way: data leaves unchecked, or people work around the ban.
Shadow AI. People paste data into private accounts, and the company finds out only when there's an incident.
Zero control
People just switch to their phone or a personal account, and now nobody can see it.
Shadow AI comes back
Security drowns in logs, legal has a GDPR problem and the works council a surveillance one.
Surveillance, not protection
You get a gateway and metrics, but no rules for who may read the content and when.
Nothing for the auditor
People keep using AI the way they do today. task2mask covers what neither a ban nor a log can:
Pricing
Within 48 hours we'll prepare a quote based on the agreed functional scope, the number of users and your channels for communicating with AI.
Features
What task2mask does today: from masking in the browser to a log that holds up in front of an auditor.
| Feature | In the platform |
|---|---|
| Interception and access | |
| Browser extension (Chrome, Safari) | |
| AI on company accounts and keys, not personal ones | |
| API gateway (OpenAI, Anthropic) | |
| Developer seats (Claude Code, Codex, Cursor) | |
| Blocking unapproved AI tools | |
| Enforced extension install (MDMCentral management of company computers: lets you install the extension on all of them at once and stop users switching it off.) | |
| Data protection | |
| Personal data and identifier masking | |
| Reversible masking | |
| Detects people, companies and addresses in text | |
| Context awareness (an invoice number isn't an ID number) | |
| Intent detection (why someone is sending the data) | |
| Company dictionary (clients, case numbers) | |
| Custom anonymiser rules, by hand and AI-generated | |
| Industry rule packs | |
| Server-side document anonymisation (Censor) | |
| Check that anonymised documents can't be re-identified | |
| Retention and erasure | |
| Policies and risk | |
| 48 built-in policy templates | |
| Custom policies | |
| Active blocking before sending (secrets, high-risk content) | |
| Prompt injectionHidden instructions in content (e.g. in a document) that try to make an AI do something unwanted. detection | |
| Conversation risk scoring and alerts | |
| AI categorisation of prompts | |
| Policies generated from regulatory documents | |
| People and process | |
| AI Academy: training and certificates | |
| Consent and transparency for employees | |
| Employee portal with access log | |
| Audit and compliance | |
| Audit log, incidents, e-mail alerts | |
| Audit sealA chain of cryptographic hashes that reveals any attempt to alter the event log. (tamper detection) | |
| Consent, retention and erasure requests (GDPR) | |
| Consent report, complaints channel, Statement of Applicability (SoA, ISO 27001) | |
| Compliance registers and evidence report: DPIA / FRIAImpact assessments: for data protection (GDPR) and for fundamental rights (AI Act)., AI ActThe EU regulation on AI; among other things it requires training and event logging. registers, complaints | |
| Auditor export | |
| Integrations and administration | |
| Webhooks (Slack, Teams, JSON) | |
| Admin via command line and AI assistant (CLI, MCP) | |
| Admin roles and MFA | |
| Backups and service monitoring | |
| Fleet management: versions and remote updates | |
| Multiple entities in one system | |
| Periodic reports | |
| Interface languages (PL, EN, CS) | |
Need integrations, a turnkey deployment or a different scope? Write to us.
In 30 minutes we'll show you how a prompt with client data reaches the AI already masked, while the log keeps a trail for the auditor. Nothing to install on your side.
Not in readable form. The AI provider only gets placeholders instead of the data, and we recognise names and scans locally.
Yes. Masking is reversible: the model works on placeholders, and the employee gets the full answer with the real data back in place.
No. People keep using ChatGPT, Gemini or Claude, but company data no longer leaves with them, and you have proof of it.
No. We only look at traffic to AI services, not the whole computer, so this isn't classic DLP.
Yes. Everyone has an employee portal with a log of access to their data, and the Pro plan adds a separate view for the works council.
We delete it from the log. The erasure itself is recorded, and the cryptographic chain still confirms that nobody changed the other entries.
You pay for ChatGPT, Gemini or Claude subscriptions or API usage directly to the provider. task2mask only charges for seats.
Any active AI user, however many devices or channels they use.
Nothing gets cut off. Once the token limit runs out, only the AI-based layers pause, and pattern-based masking keeps working. If you go over your plan's seat count, you have 30 days to adjust the plan. Everything keeps working in the meantime, and extra seats are billed only at renewal.
Depending on scope: from a self-service start to deployment run by our team. We set the scope and cost of deployment in the quote.
Yes, 30 days for up to 10 seats, no card required. We agree the trial details in the quote.